Showing posts with label VPN. Show all posts

CCIE Security Lab: ASA to IOS IKEv1 tunnel

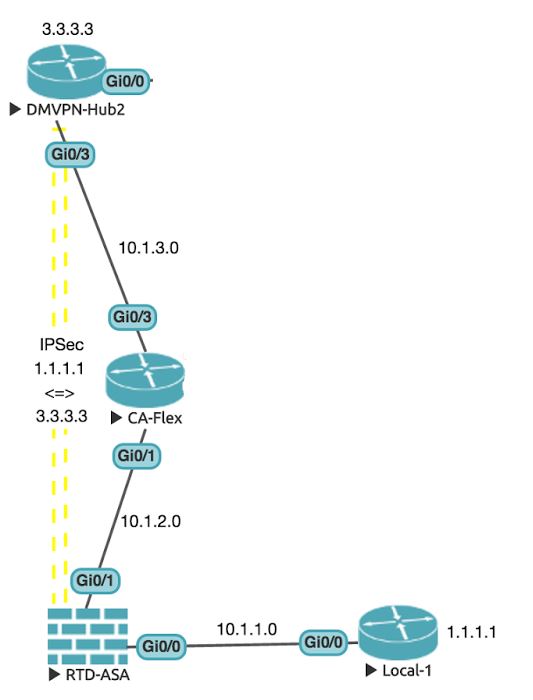
In the first part of the new VPN topology, I will be looking at connecting up the lower left-hand side routers, using a mix of static routes and OSPF to get them talking, and then setting up an IPSec VPN between the ASA and DMVPN-Hub2.
Cisco ASA to IOS IPSec VPNs

We will start with the basic connectivity. Using static routing to send all of Local-1's traffic to the ASA, and then OSPF to bridge the rest of the network.

You can find most of the steps in the link for ASA to IOS IKEv1.

Basic OSPF

The OSPf setup here is nothing special, everything is going into Area 0:
RTD-ASA# sh int ip bri | e unas
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0         10.1.1.254      YES manual up                    up  
GigabitEthernet0/1         10.1.2.254      YES manual up                    up  
RTD-ASA#

Local-1#sh ip int bri | e unas
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0         10.1.1.1        YES manual up                    up      
Loopback0                  1.1.1.1         YES manual up                    up      
Local-1#

Local-1(config)#ip route 0.0.0.0 0.0.0.0 10.1.1.254
Local-1(config)#


RTD-ASA(config)# route inside 1.1.1.1 255.255.255.255 10.1.1.1
RTD-ASA(config)#
RTD-ASA(config)# router ospf 1
RTD-ASA(config-router)# network 10.1.2.0 255.255.255.0 area 0
RTD-ASA(config-router)# red static subnets
RTD-ASA(config-router)# 

CA-Flex(config)#do sh ip int bri | e unas
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/1         10.1.2.2        YES manual up                    up      
GigabitEthernet0/3         10.1.3.2        YES manual up                    up      
Loopback0                  2.2.2.2         YES manual up                    up      

CA-Flex(config)#router ospf 1
CA-Flex(config-router)#router-id 2.2.2.2
CA-Flex(config-router)#network 10.1.2.0 0.255.255.255 area 0
CA-Flex(config-router)#                              
CA-Flex(config-router)#network 10.1.3.0 0.255.255.255 area 0
CA-Flex(config-router)#

DMVPN-Hub2(config)#do sh ip int bri | e unas
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0         10.1.5.3        YES manual up                    up      
GigabitEthernet0/3         10.1.3.3        YES manual up                    up      
Loopback0                  3.3.3.3         YES manual up                    up      

DMVPN-Hub2(config)#router ospf 1
DMVPN-Hub2(config-router)#router-id 3.3.3.3
DMVPN-Hub2(config-router)#network 10.1.3.0 0.255.255.255 area 0
DMVPN-Hub2(config-router)#
%OSPF-5-ADJCHG: Process 1, Nbr 2.2.2.2 on GigabitEthernet0/3 from LOADING to FULL, Loading Done
DMVPN-Hub2(config-router)#
Now that we have this done, we can set up the VPN tunnel.

IKEv1 IPSec tunnel between ASA and IOS

Now we set up the VPN tunnel. It won't work straight away, and this is (partially) intentional. I need to be hot on the debugging of VPN failures for the exam, that said, I don't want to spend too much time troubleshooting in the lab!

The first step is to create the access lists to define our interesting traffic:
RTD-ASA(config)# access-list IPSec-VPN-Traffic extended permit ip host 1.1.1.1 host 3.3.3.3

DMVPN-Hub2(config)#access-list 101 permit ip host 3.3.3.3 host 1.1.1.1
DMVPN-Hub2(config)#
We then create the ISAKMP policy:
RTD-ASA(config)# crypto isakmp policy 10
RTD-ASA(config-ikev1-policy)# encryption 3des
RTD-ASA(config-ikev1-policy)# auth pre-share 
RTD-ASA(config-ikev1-policy)# group 2
RTD-ASA(config-ikev1-policy)# 

DMVPN-Hub2(config)#crypto isakmp policy 10
DMVPN-Hub2(config-isakmp)#encr 3des
DMVPN-Hub2(config-isakmp)#auth pre-share 
DMVPN-Hub2(config-isakmp)#group 2
DMVPN-Hub2(config-isakmp)#
Next we create the transform set
RTD-ASA(config)# crypto ipsec transform-set VPN-transforms esp-3des esp-sha-hmac
RTD-ASA(config)# 

DMVPN-Hub2(config)#crypto ipsec transform-set VPN-transforms esp-3des esp-sha-hmac     
DMVPN-Hub2(cfg-crypto-trans)#exit
DMVPN-Hub2(config)#
Then we create the crypto maps (defining our peers, and utilizing the transform set created earlier):
RTD-ASA(config)# crypto map VPN_Map 1 set peer 10.1.3.3
RTD-ASA(config)# crypto map VPN_Map 1 set ikev1 transform-set VPN-transforms
RTD-ASA(config)# crypto map VPN_Map 1 set ikev2 pre-shared-key cisco
RTD-ASA(config)# crypto map VPN_Map 1 match address IPSec-VPN-Traffic
RTD-ASA(config)# 
RTD-ASA(config)# crypto map VPN_Map interface Outside
RTD-ASA(config)# 
RTD-ASA(config)# tunnel-group 10.1.3.3 type ipsec-l2l 
RTD-ASA(config)# tunnel-group 10.1.3.3 ipsec-attributes 
RTD-ASA(config-tunnel-ipsec)# ikev1 pre-shared-key cisco
RTD-ASA(config-tunnel-ipsec)# 

DMVPN-Hub2(config)#crypto keyring VPN_Keys
DMVPN-Hub2(conf-keyring)#pre-shared-key address 10.1.2.254 key cisco
DMVPN-Hub2(conf-keyring)#exit
DMVPN-Hub2(config)#
DMVPN-Hub2(config)#crypto isakmp profile VPN_Map 
% A profile is deemed incomplete until it has match identity statements
DMVPN-Hub2(conf-isa-prof)#match identity address 10.1.2.254 255.255.255.255
DMVPN-Hub2(conf-isa-prof)#keyring VPN_Keys
DMVPN-Hub2(conf-isa-prof)#exit
DMVPN-Hub2(config)#
DMVPN-Hub2(config)#crypto map VPN_Map 1 ipsec-isakmp
% NOTE: This new crypto map will remain disabled until a peer
        and a valid access list have been configured.
DMVPN-Hub2(config-crypto-map)#set peer 10.1.2.254
DMVPN-Hub2(config-crypto-map)#set transform-set VPN-transforms
DMVPN-Hub2(config-crypto-map)#set isakmp-profile VPN_Map
DMVPN-Hub2(config-crypto-map)#match address 101
DMVPN-Hub2(config-crypto-map)#int gi 0/3
DMVPN-Hub2(config-if)#crypto map VPN_Map
DMVPN-Hub2(config-if)#
*Jun 26 07:59:10.158: %CRYPTO-6-ISAKMP_ON_OFF: ISAKMP is ON
DMVPN-Hub2(config-if)#
As it stands, we can bring up the tunnel by pinging 1.1.1.1 from DMVPN-Hub2 by setting the source as lo0:
DMVPN-Hub2#ping 1.1.1.1 so lo0
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 1.1.1.1, timeout is 2 seconds:
Packet sent with a source address of 3.3.3.3 
.....
Success rate is 0 percent (0/5)
DMVPN-Hub2#

RTD-ASA# sh crypto isakmp sa

IKEv1 SAs:

   Active SA: 1
    Rekey SA: 0 (A tunnel will report 1 Active and 1 Rekey SA during rekey)
Total IKE SA: 1

1   IKE Peer: 10.1.3.3
    Type    : L2L             Role    : responder 
    Rekey   : no              State   : MM_ACTIVE 

There are no IKEv2 SAs
RTD-ASA# 

DMVPN-Hub2#sh crypto isakmp sa
IPv4 Crypto ISAKMP SA
dst             src             state          conn-id status
10.1.2.254      10.1.3.3        QM_IDLE           1001 ACTIVE

IPv6 Crypto ISAKMP SA

DMVPN-Hub2#
We have the right details above. The ASA should show MM_ACTIVE, and the IOS route should show "QM_IDLE". We will not get a response yet as RTD-ASA is not set up yet. We still need to set up NAT, and a NAT exemption for the 1.1.1.1 address.

We do want to NAT the 10.1.1.1 subnet, but not the 1.1.1.1 subnet, so let's set that up as well.

We start by creating three objects, one for the network we will want to NAT (10.1.1.0/24), one for the host we do not want to NAT for internally (1.1.1.1) and one for the host we will not want to NAT for externally (3.3.3.3):
RTD-ASA(config)# object network Nat-Networks
RTD-ASA(config-network-object)# subnet 10.1.1.0 255.255.255.0
RTD-ASA(config-network-object)# exit
RTD-ASA(config)# object network No-Nat-Networks
RTD-ASA(config-network-object)# host 1.1.1.1
RTD-ASA(config-network-object)# exit
RTD-ASA(config)# object network No-Nat-Destination
RTD-ASA(config-network-object)# host 3.3.3.3
RTD-ASA(config-network-object)# exit
The we can use these objects in the NAT rule:
RTD-ASA(config)# terminal width 255
RTD-ASA(config)# nat (inside,outside) source static No-Nat-Networks No-Nat-Networks destination static No-Nat-Destination No-Nat-Destination no-proxy-arp route-lookup
RTD-ASA(config)# 
Does it work now?
Local-1#ping 3.3.3.3 so lo0
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 3.3.3.3, timeout is 2 seconds:
Packet sent with a source address of 1.1.1.1 
.....
Success rate is 0 percent (0/5)
Local-1#
Not so far. Let's dig in:
RTD-ASA# sh crypto ipsec sa
interface: Outside
    Crypto map tag: VPN_Map, seq num: 1, local addr: 10.1.2.254

      access-list IPSec-VPN-Traffic extended permit ip host 1.1.1.1 host 3.3.3.3 
      local ident (addr/mask/prot/port): (1.1.1.1/255.255.255.255/0/0)
      remote ident (addr/mask/prot/port): (3.3.3.3/255.255.255.255/0/0)
      current_peer: 10.1.3.3


      #pkts encaps: 0, #pkts encrypt: 0, #pkts digest: 0 <== Nothing being transmitted!
      #pkts decaps: 14, #pkts decrypt: 14, #pkts verify: 14
      #pkts compressed: 0, #pkts decompressed: 0
      #pkts not compressed: 0, #pkts comp failed: 0, #pkts decomp failed: 0
      #pre-frag successes: 0, #pre-frag failures: 0, #fragments created: 0
      #PMTUs sent: 0, #PMTUs rcvd: 0, #decapsulated frgs needing reassembly: 0
      #TFC rcvd: 0, #TFC sent: 0
      #Valid ICMP Errors rcvd: 0, #Invalid ICMP Errors rcvd: 0
      #send errors: 0, #recv errors: 0

      local crypto endpt.: 10.1.2.254/0, remote crypto endpt.: 10.1.3.3/0
      path mtu 1500, ipsec overhead 58(36), media mtu 1500
      PMTU time remaining (sec): 0, DF policy: copy-df
      ICMP error validation: disabled, TFC packets: disabled
      current outbound spi: 45623476
      current inbound spi : 26AD8AD7

    inbound esp sas:
      spi: 0x26AD8AD7 (648907479)
         transform: esp-3des esp-sha-hmac no compression 
         in use settings ={L2L, Tunnel, IKEv1, }
         slot: 0, conn_id: 8192, crypto-map: VPN_Map
         sa timing: remaining key lifetime (kB/sec): (3914998/2623)
         IV size: 8 bytes
         replay detection support: Y
         Anti replay bitmap: 
          0x00000000 0x00007FFF
    outbound esp sas:
      spi: 0x45623476 (1164063862)
         transform: esp-3des esp-sha-hmac no compression 
         in use settings ={L2L, Tunnel, IKEv1, }
         slot: 0, conn_id: 8192, crypto-map: VPN_Map
         sa timing: remaining key lifetime (kB/sec): (3915000/2622)
         IV size: 8 bytes
         replay detection support: Y
         Anti replay bitmap: 
          0x00000000 0x00000001

RTD-ASA#
We are not transmitting any packets. Why is this?
RTD-ASA(config)# logging console 7
RTD-ASA(config)# logging on
%ASA-5-111008: User 'enable_15' executed the 'logging on' command.
RTD-ASA(config)# 
%ASA-5-111010: User 'enable_15', running 'CLI' from IP 0.0.0.0, executed 'logging on'
%ASA-7-609001: Built local-host Outside:3.3.3.3
%ASA-7-609001: Built local-host Inside:1.1.1.1
%ASA-6-302020: Built inbound ICMP connection for faddr 3.3.3.3/4 gaddr 1.1.1.1/0 laddr 1.1.1.1/0
%ASA-6-110002: Failed to locate egress interface for ICMP from Inside:1.1.1.1/0 to 3.3.3.3/4
%ASA-6-302021: Teardown ICMP connection for faddr 3.3.3.3/4 gaddr 1.1.1.1/0 laddr 1.1.1.1/0
%ASA-7-609002: Teardown local-host Outside:3.3.3.3 duration 0:00:10
%ASA-7-609002: Teardown local-host Inside:1.1.1.1 duration 0:00:10
The clue here is "Failed to locate egress interface", meaning we do not have a route to the destination. Let's add one, and see if this solves the issue:
DMVPN-Hub2(config)#router ospf 1
DMVPN-Hub2(config-router)#network 3.3.3.3 0.0.0.0 area 1 
DMVPN-Hub2(config-router)#
Does it work now?
Local-1#ping 3.3.3.3 so lo0
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 3.3.3.3, timeout is 2 seconds:
Packet sent with a source address of 1.1.1.1 
.!!!!
Success rate is 80 percent (4/5), round-trip min/avg/max = 9/10/12 ms
Local-1#
It does. We are also encrypting as much traffic as we are decrypting:
RTD-ASA# sh vpn-sessiondb detail l2l 

Session Type: LAN-to-LAN Detailed

Connection   : 10.1.3.3
Index        : 3                      IP Addr      : 10.1.3.3
Protocol     : IKEv1 IPsec
Encryption   : IKEv1: (1)3DES  IPsec: (1)3DES
Hashing      : IKEv1: (1)SHA1  IPsec: (1)SHA1
Bytes Tx     : 400                    Bytes Rx     : 400
Login Time   : 21:51:24 UTC Mon Jun 27 2016
Duration     : 0h:01m:27s

IKEv1 Tunnels: 1
IPsec Tunnels: 1

IKEv1:
  Tunnel ID    : 3.1
  UDP Src Port : 500                    UDP Dst Port : 500
  IKE Neg Mode : Main                   Auth Mode    : preSharedKeys
  Encryption   : 3DES                   Hashing      : SHA1
  Rekey Int (T): 86400 Seconds          Rekey Left(T): 86313 Seconds
  D/H Group    : 2
  Filter Name  : 

IPsec:        
  Tunnel ID    : 3.2
  Local Addr   : 1.1.1.1/255.255.255.255/0/0
  Remote Addr  : 3.3.3.3/255.255.255.255/0/0
  Encryption   : 3DES                   Hashing      : SHA1                   
  Encapsulation: Tunnel                 
  Rekey Int (T): 3600 Seconds           Rekey Left(T): 3513 Seconds           
  Rekey Int (D): 4608000 K-Bytes        Rekey Left(D): 4608000 K-Bytes        
  Idle Time Out: 30 Minutes             Idle TO Left : 28 Minutes             
  Bytes Tx     : 400                    Bytes Rx     : 400                    
  Pkts Tx      : 4                      Pkts Rx      : 4                      
  
RTD-ASA#
Perfect! Logging everything on the console probably isn't the best idea, though. On a small-scale like this it's fine, but in a busy production environment, it would be easy to miss important information. In a lab exam, it's fine, just so long as you remember to remove the logging commands that were added. So, do we have a neater method?

Let's remove the route and find out
DMVPN-Hub2(config)#router ospf 1
DMVPN-Hub2(config-router)#no network 3.3.3.3 0.0.0.0 area 1
DMVPN-Hub2(config-router)#

RTD-ASA# sh route | b Gate
Gateway of last resort is not set

S        1.1.1.1 255.255.255.255 [1/0] via 10.1.1.1, Inside
C        10.1.1.0 255.255.255.0 is directly connected, Inside
L        10.1.1.254 255.255.255.255 is directly connected, Inside
C        10.1.2.0 255.255.255.0 is directly connected, Outside
L        10.1.2.254 255.255.255.255 is directly connected, Outside
O        10.1.3.0 255.255.255.0 [110/11] via 10.1.2.2, 1d14h, Outside
O        10.1.5.0 255.255.255.0 [110/12] via 10.1.2.2, 1d14h, Outside

RTD-ASA# 
Now, using the packet-tracer command, we can see the error:
RTD-ASA# packet-tracer input Inside icmp 1.1.1.1 8 0 3.3.3.3         

Phase: 1
Type: ACCESS-LIST
Subtype: 
Result: ALLOW
Config:
Implicit Rule
Additional Information:
MAC Access list

Result:
input-interface: Inside
input-status: up
input-line-status: up
Action: drop
Drop-reason: (no-route) No route to host

RTD-ASA# 
We can also append the "detailed" keyword to get more information, but in this case, we just get a more succint output:
RTD-ASA# packet-tracer input Inside icmp 1.1.1.1 8 0 3.3.3.3 detailed

Result:
input-interface: Inside
input-status: up
input-line-status: up
Action: drop
Drop-reason: (no-route) No route to host

RTD-ASA# 
So, we can use this command, instead of enabling logging. For the moment, though, we'll just add the route back, and get the connectivity back:
DMVPN-Hub2(config)#router ospf 1
DMVPN-Hub2(config-router)#network 3.3.3.3 0.0.0.0 area 1
DMVPN-Hub2(config-router)#

Local-1#ping 3.3.3.3 so lo0
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 3.3.3.3, timeout is 2 seconds:
Packet sent with a source address of 1.1.1.1 
.!!!!
Success rate is 80 percent (4/5), round-trip min/avg/max = 9/9/10 ms
Local-1#
Throughout this post, when we have looked at the output of "show crypto isakmp sa" we have been told that "There are no IKEv2 SAs". In the next post we will set up IKEv2.

UNetLab topologies now available.

It seems that (and I am very thankful for this) UNetLab is making strong gains in popularity, as it should.

Whilst I do get the occasional email asking for setup help with GNS3 (which I am more than happy to do), I get far more emails asking when the book topologies will be available for UNetLab.

So, now that things have quietened down a bit, I have had time to do this.

On the relevant pages (above, under the Books menu) there are links for the files for the main topologies for all the books.

They are also here, to make it easier.

To import them you just need to create a folder called 802101 (you don't really have to have a folder, but it makes it neater):


Once thats done, go into the folder and then import an external object. Make sure its the whole zip file!


Then you should get a nice bunch of new labs:


The download links are below.

UNetLab Topology download links:

BGP for Cisco Networks
MPLS for Cisco Networks
VPNs and NAT for Cisco Networks

How to NAT private IP address within a VPN

Continuing from the little lab I built up in the last post, where I looked at how to get Windows 7 running natively in UNetLab, I now am looking at how we can perform NAT inside of an IPSec tunnel.

I am using the following for this:

2x Windows 7 (Pro), with VLC, Putty, JRE and ASDM installed
2x IOSv Layer 2 switches (running 15.2)
2x ASAv (running 9.4(1))
1x IOSv (running 15.5) - AKA "Internet".

All of these are within UNetLab, which is, so far, coping nicely with just the 8GB ram that Fusion seems to allow, but I really should put it on my ESXi server. I have seen ways to get around the 8GB limit, but every time I try, Fusion says its unsupported, and drops it down to 32Kb. It's a challenge.

The topology looks like this (note not everything is started just yet):


The end goal is that we have a VPN between the two ASAs, with HQ performing NAT to mask the traffic inside the VPN tunnel. You may be asking "Why the hell would you ever need to do that?", and it's a very good question, really it's not something you'd have to do often, but there are those times when someone doesn't like RFC1918 addresses going across a VPN tunnel, or (more commonly) you need to VPN to another site that has overlapping internal subnets.

Basic IP addressing (all /24):

Interface IP Address
DMZ-Server10.1.1.10 (default gateway 10.1.1.254)
HQ Gi0/310.1.1.1
HQ Gi0/11.1.1.2
Internet Gi0/01.1.1.1
Internet Gi0/12.2.2.1
Client Gi0/12.2.2.2
Client Gi0/3 10.200.1.1
Client-PC 10.200.1.10 (default gateway 10.200.1.254)

HQ Switch configuration

Very basic, just one vlan, and a VIF:
Switch#sh vlan | i VLAN0011
11   VLAN0011                         active    Gi0/0, Gi0/1, Gi0/2, Gi0/3
Switch#sh ip int bri | e unas
Interface              IP-Address      OK? Method Status                Protocol
Vlan11                 10.1.1.254      YES manual up                    up      

Switch#

Basic (HQ) ASA setup.

Below is enough to get us started, and onto ASDM from our DMZ-Server:
hostname HQ
!
interface GigabitEthernet0/1
 nameif Outside
 security-level 0
 ip address 1.1.1.2 255.255.255.0 
!
interface GigabitEthernet0/3
 nameif DMZ
 security-level 50
 ip address 10.1.1.1 255.255.255.0 
!
same-security-traffic permit inter-interface
same-security-traffic permit intra-interface
!
route Outside 0.0.0.0 0.0.0.0 1.1.1.1 1
!
user-identity default-domain LOCAL
aaa authentication enable console LOCAL 
aaa authentication http console LOCAL 
aaa authentication ssh console LOCAL 
http server enable
http 10.1.1.0 255.255.255.0 DMZ
!
ssh 1.1.1.1 255.255.255.255 Outside
ssh 10.1.1.0 255.255.255.0 DMZ
ssh timeout 5
ssh version 2
ssh key-exchange group dh-group1-sha1
!
username stuart password p60UDLdMNnbR8IQ. encrypted
!

The set-up for the Client ASA is not much different, and similarly, on the Client switch we have one VLAN (200), and a VIF of 10.200.1.254:
Switch#sh vlan | i VLAN0200  
200  VLAN0200                         active    Gi0/0, Gi0/1, Gi0/2, Gi0/3
Switch#sh ip int bri | e unas
Interface              IP-Address      OK? Method Status                Protocol
Vlan200                10.200.1.254    YES manual up                    up      

Switch#

So far we should be able to ping from our Windows PCs to our ASAs:


Basic Internet access (our first NAT).

On the Internet router, we have a loopback interface with the IP address 8.8.8.8/32. We should be able to give ourselves access to this. It's working directly from the HQ ASA at the moment:
HQ# ping 8.8.8.8
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 8.8.8.8, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 10/10/10 ms
HQ# 
The first NAT rule "connects" the DMZ interface to the Outside interface:
HQ(config)# nat (DMZ,Outside) after-auto source dynamic any interface 
HQ(config)# 
If we follow it through, we can see that the rule will be placed last in the NAT rules table (after-auto). We match the DMZ and the Outside interfaces (our source network and the one we want to get to). We set a source of dynamic, meaning we can have more than one host behind this network, and we allow any source using the "any" keyword. Lastly we nat this through to the interface IP address given to our Outside interface.

I did have to use the command "fixup protocol icmp" in order to get the ping to work. The ASA will convert this into the following command:
HQ(config)# policy-map global_policy
HQ(config-pmap)# class inspection_default
HQ(config-pmap-c)# inspect icmp
HQ(config-pmap-c)# 
So now we also have "Internet" access (to a loopback on the Internet router):


Let's go ahead and set up the other side, and make sure that they can also ping the "Internet":
Client# ping 8.8.8.8
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 8.8.8.8, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 10/14/30 ms
Client#conf t
Client(config)# policy-map global_policy
Client(config-pmap)# class  inspection_default
Client(config-pmap-c)# inspect icmp
Client(config-pmap-c)# exit
Client(config-pmap)#exit
Client(config)# nat (Inside,Outside) source  dynamic any interf
Client(config)# 
Great! Now the client should have access:


Now we can begin to create our VPN between the two sides.

Site-to-Site (L2L) IPSec VPN on Cisco ASAs

We start with a couple of network objects, and an access-list:
Client(config)# object network MyInsideNetwork
Client(config-network-object)# subnet 10.200.1.0 255.255.255.0
Client(config-network-object)# exit
Client(config)# object network TheirRemoteNetwork
Client(config-network-object)# subnet 10.1.1.0 255.255.255.0
Client(config-network-object)# exit
Client(config)# access-list Outside_cryptomap extended permit ip object MyInsideNetwork object TheirRemoteNetwork
Now we can start to define how we are going to talk to other peers:
Client(config)# nat (Inside,Outside) source static MyInsideNetwork MyInsideNetwork destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
Client(config)#crypto ipsec ikev1 transform-set ESP-AES-128-SHA esp-aes esp-sha-hmac
Client(config)# crypto ipsec ikev2 ipsec-proposal AES256
Client(config-ipsec-proposal)# protocol esp encryption aes-256
Client(config-ipsec-proposal)# protocol esp integrity sha-1 md5
Client(config-ipsec-proposal)# exi
Client(config)# crypto ikev2 policy 1 
Client(config-ikev2-policy)# encryption aes-256
Client(config-ikev2-policy)# integrity sha
Client(config-ikev2-policy)# group 2
Client(config-ikev2-policy)# prf sha
Client(config-ikev2-policy)# lifetime seconds 86400
Client(config-ikev2-policy)# exi
Client(config)# crypto ikev1 policy 10
Client(config-ikev1-policy)# authentication pre-share 
Client(config-ikev1-policy)# encryption aes-256 
Client(config-ikev1-policy)# hash sha
Client(config-ikev1-policy)# group 2
Client(config-ikev1-policy)# lifetime 86400
Client(config-ikev1-policy)# exi
Client(config)# crypto ikev2 enable Outside
Client(config)# crypto ikev1 enable Outside
Client(config)# 
Then we create the VPN, trying to keep it as generic as possible so that it is nice and easy to paste onto our other ASA:
Client(config)# crypto map Outside_map 1 match address Outside_cryptomap
Client(config)# crypto map Outside_map 1 set peer 1.1.1.2               
Client(config)# crypto map Outside_map 1 set ikev1 transform-set ESP-AES-128-SHA
Client(config)# crypto map Outside_map 1 set ikev2 ipsec-proposal AES256
Client(config)# crypto map Outside_map interface Outside               
Client(config)# group-policy MyPeer internal             
Client(config)# group-policy MyPeer attributes 
Client(config-group-policy)# vpn-tunnel-protocol ikev1 ikev2
Client(config-group-policy)# tunnel-group 1.1.1.2 type ipsec-l2l   
Client(config)# tunnel-group 1.1.1.2 general-attributes 
Client(config-tunnel-general)# default-group-policy MyPeer
Client(config-tunnel-general)# exi
Client(config)# tunnel-group 1.1.1.2 ipsec-attributes 
Client(config-tunnel-ipsec)# ikev1 pre-shared-key MyKey
Client(config-tunnel-ipsec)# ikev2 remote-authentication pre-shared-key MyKey
INFO: You must configure ikev2 local-authentication pre-shared-key
      or certificate to complete authentication.
Client(config-tunnel-ipsec)# ikev2 local-authentication pre-shared-key MyKey
Client(config-tunnel-ipsec)# 
Moving on to the other (HQ) ASA, we can (with a minor edit here and there) paste in the same config:
HQ(config)# object network MyInsideNetwork
HQ(config-network-object)# subnet 10.1.1.0 255.255.255.0
HQ(config-network-object)# exit
HQ(config)# object network TheirRemoteNetwork
HQ(config-network-object)# subnet 10.200.1.0 255.255.255.0
HQ(config-network-object)# exit
HQ(config)# access-list Outside_cryptomap extended permit ip object MyInsideNetwork object TheirRemoteNetwork
HQ(config)# nat (Inside,Outside) source static MyInsideNetwork MyInsideNetwork destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
HQ(config)# crypto ipsec ikev1 transform-set ESP-AES-128-SHA esp-aes esp-sha-hmac
HQ(config)# crypto ipsec ikev2 ipsec-proposal AES256
HQ(config-ipsec-proposal)# protocol esp encryption aes-256
HQ(config-ipsec-proposal)# protocol esp integrity sha-1 md5
HQ(config-ipsec-proposal)# exi
HQ(config)# crypto ikev2 policy 1 
HQ(config-ikev2-policy)# encryption aes-256
HQ(config-ikev2-policy)# integrity sha
HQ(config-ikev2-policy)# group 2
HQ(config-ikev2-policy)# prf sha
HQ(config-ikev2-policy)#  lifetime seconds 86400
HQ(config-ikev2-policy)# exi
HQ(config)# crypto ikev1 policy 10
HQ(config-ikev1-policy)# authentication pre-share 
HQ(config-ikev1-policy)# encryption aes-256 
HQ(config-ikev1-policy)# hash sha
HQ(config-ikev1-policy)# group 2
HQ(config-ikev1-policy)# lifetime 86400
HQ(config-ikev1-policy)# exi
HQ(config)# crypto ikev2 enable Outside
HQ(config)# crypto ikev1 enable Outside
HQ(config)# crypto map Outside_map 1 match address Outside_cryptomap
HQ(config)# crypto map Outside_map 1 set peer 2.2.2.2               
HQ(config)# crypto map Outside_map 1 set ikev1 transform-set ESP-AES-128-SHA
HQ(config)# crypto map Outside_map 1 set ikev2 ipsec-proposal AES256
HQ(config)# crypto map Outside_map interface Outside               
HQ(config)# group-policy MyPeer internal             
HQ(config)# group-policy MyPeer attributes 
HQ(config-group-policy)# vpn-tunnel-protocol ikev1 ikev2
HQ(config-group-policy)# tunnel-group 2.2.2.2 type ipsec-l2l   
HQ(config)# tunnel-group 2.2.2.2 general-attributes 
HQ(config-tunnel-general)# default-group-policy MyPeer
HQ(config-tunnel-general)# exi
HQ(config)# tunnel-group 2.2.2.2 ipsec-attributes 
HQ(config-tunnel-ipsec)#  ikev1 pre-shared-key MyKey
HQ(config-tunnel-ipsec)# ikev2 remote-authentication pre-shared-key MyKey
INFO: You must configure ikev2 local-authentication pre-shared-key
      or certificate to complete authentication.
HQ(config-tunnel-ipsec)# ikev2 local-authentication pre-shared-key MyKey
HQ(config-tunnel-ipsec)# 
And boom! We have a working VPN:


Traffic works the other way as well.


OK, so now that we have a working VPN, let's see if we can NAT on the HQ side.

NAT and Site-to-Site VPNs

In order that we can hide our 10.1.1.0/24 network behind a new network (192.168.1.0/24), we need to add another network object to HQ, add a NAT rule, an access-list, and finally edit our crypto map to reference the access-list:
HQ(config)# object network YouSeeMeAs
HQ(config-network-object)# subnet 192.168.1.0 255.255.255.0
HQ(config-network-object)# exi
HQ(config)#nat (DMZ,Outside) source static MyInsideNetwork YouSeeMeAs destination static TheirRemoteNetwork TheirRemoteNetwork
HQ(config)#access-list Hidden_CryptoMap extended permit ip object YouSeeMeAs object TheirRemoteNetwork
HQ(config)#crypto map Outside_map 1 match address Hidden_CryptoMap
Now we need to change the other side to look towards the 192.168.1.0 traffic (instead of the 10.1.1.0/24 network):


Once we send some traffic between the two sites, our VPN should get established.


Quite nicely, it's preserving (or reserving) the final octet for us. However, we are now only good for being called into. Our pings from HQ to the Client fail:


OK, so how do we get both sides working, instead of this one-way traffic that we have? Well, let's try and work out what's happening.
HQ# sh nat detail 
Manual NAT Policies (Section 1)
1 (DMZ) to (Outside) source static MyInsideNetwork MyInsideNetwork   destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
    translate_hits = 32, untranslate_hits = 32
    Source - Origin: 10.1.1.0/24, Translated: 10.1.1.0/24
    Destination - Origin: 10.200.1.0/24, Translated: 10.200.1.0/24
2 (DMZ) to (Outside) source static MyInsideNetwork YouSeeMeAs   destination static TheirRemoteNetwork TheirRemoteNetwork
    translate_hits = 7, untranslate_hits = 7
    Source - Origin: 10.1.1.0/24, Translated: 192.168.1.0/24
    Destination - Origin: 10.200.1.0/24, Translated: 10.200.1.0/24

Manual NAT Policies (Section 3)
1 (DMZ) to (Outside) source dynamic any interface  
    translate_hits = 66, untranslate_hits = 59
    Source - Origin: 0.0.0.0/0, Translated: 1.1.1.2/24
HQ# 
This is our NAT table. And here is a very long packet-tracer output:
HQ# packet-tracer input DMZ icmp 10.1.1.10 1 7 10.200.1.10 detailed 

Phase: 1
Type: ROUTE-LOOKUP
Subtype: Resolve Egress Interface
Result: ALLOW
Config:
Additional Information:
found next-hop 1.1.1.1 using egress ifc  Outside

Phase: 2
Type: UN-NAT
Subtype: static
Result: ALLOW
Config:
nat (DMZ,Outside) source static MyInsideNetwork MyInsideNetwork destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
Additional Information:
NAT divert to egress interface Outside
Untranslate 10.200.1.10/0 to 10.200.1.10/0

Phase: 3
Type: ACCESS-LIST
Subtype: log
Result: ALLOW
Config:
access-group DMZ_access_in in interface DMZ
access-list DMZ_access_in extended permit object-group DM_INLINE_SERVICE_1 any any 
object-group service DM_INLINE_SERVICE_1
 service-object ip 
 service-object icmp 
 service-object icmp echo
 service-object icmp echo-reply
Additional Information:
 Forward Flow based lookup yields rule:
 in  id=0x7fffcd5403e0, priority=13, domain=permit, deny=false
        hits=48, user_data=0x7fffd8e59d00, cs_id=0x0, use_real_addr, flags=0x0, protocol=0
        src ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any
        dst ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any, dscp=0x0
        input_ifc=DMZ, output_ifc=any

Phase: 4
Type: NAT
Subtype: 
Result: ALLOW
Config:
nat (DMZ,Outside) source static MyInsideNetwork MyInsideNetwork destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
Additional Information:
Static translate 10.1.1.10/0 to 10.1.1.10/0
 Forward Flow based lookup yields rule:
 in  id=0x7fffce1821f0, priority=6, domain=nat, deny=false
        hits=29, user_data=0x7fffce14e060, cs_id=0x0, flags=0x0, protocol=0
        src ip/id=10.1.1.0, mask=255.255.255.0, port=0, tag=any
        dst ip/id=10.200.1.0, mask=255.255.255.0, port=0, tag=any, dscp=0x0
        input_ifc=DMZ, output_ifc=Outside

Phase: 5
Type: NAT
Subtype: per-session
Result: ALLOW
Config:
Additional Information:
 Forward Flow based lookup yields rule:
 in  id=0x7fffcd2d74f0, priority=0, domain=nat-per-session, deny=true
        hits=270, user_data=0x0, cs_id=0x0, reverse, use_real_addr, flags=0x0, protocol=0
        src ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any
        dst ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any, dscp=0x0
        input_ifc=any, output_ifc=any

Phase: 6
Type: IP-OPTIONS
Subtype: 
Result: ALLOW 
Config:
Additional Information:
 Forward Flow based lookup yields rule:
 in  id=0x7fffcdabbd30, priority=0, domain=inspect-ip-options, deny=true
        hits=522, user_data=0x0, cs_id=0x0, reverse, flags=0x0, protocol=0
        src ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any
        dst ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any, dscp=0x0
        input_ifc=DMZ, output_ifc=any

Phase: 7
Type: QOS
Subtype: 
Result: ALLOW
Config:
Additional Information:
 Forward Flow based lookup yields rule:
 in  id=0x7fffcd9ecd50, priority=70, domain=qos-per-class, deny=false
        hits=191, user_data=0x7fffcd9eca20, cs_id=0x0, reverse, use_real_addr, flags=0x0, protocol=0
        src ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any
        dst ip/id=0.0.0.0, mask=0.0.0.0, port=0, tag=any, dscp=0x0
        input_ifc=any, output_ifc=any

Phase: 8      
Type: INSPECT
Subtype: np-inspect
Result: ALLOW
Config:
class-map inspection_default
 match default-inspection-traffic
policy-map global_policy
 class inspection_default
  inspect icmp 
service-policy global_policy global
Additional Information:
 Forward Flow based lookup yields rule:
 in  id=0x7fffcda4d390, priority=70, domain=inspect-icmp, deny=false
        hits=44, user_data=0x7fffce13f110, cs_id=0x0, use_real_addr, flags=0x0, protocol=1
        src ip/id=0.0.0.0, mask=0.0.0.0, icmp-type=0, tag=any
        dst ip/id=0.0.0.0, mask=0.0.0.0, icmp-code=0, tag=any, dscp=0x0
        input_ifc=DMZ, output_ifc=any

Phase: 9
Type: INSPECT
Subtype: np-inspect
Result: ALLOW
Config:       
Additional Information:
 Forward Flow based lookup yields rule:
 in  id=0x7fffcdabb5e0, priority=66, domain=inspect-icmp-error, deny=false
        hits=128, user_data=0x7fffcdabab40, cs_id=0x0, use_real_addr, flags=0x0, protocol=1
        src ip/id=0.0.0.0, mask=0.0.0.0, icmp-type=0, tag=any
        dst ip/id=0.0.0.0, mask=0.0.0.0, icmp-code=0, tag=any, dscp=0x0
        input_ifc=DMZ, output_ifc=any

Phase: 10
Type: NAT
Subtype: rpf-check
Result: ALLOW
Config:
nat (DMZ,Outside) source static MyInsideNetwork MyInsideNetwork destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
Additional Information:
 Forward Flow based lookup yields rule:
 out id=0x7fffce182df0, priority=6, domain=nat-reverse, deny=false
        hits=29, user_data=0x7fffce14e160, cs_id=0x0, use_real_addr, flags=0x0, protocol=0
        src ip/id=10.1.1.0, mask=255.255.255.0, port=0, tag=any
        dst ip/id=10.200.1.0, mask=255.255.255.0, port=0, tag=any, dscp=0x0
        input_ifc=DMZ, output_ifc=Outside

Phase: 11     
Type: FLOW-CREATION
Subtype: 
Result: ALLOW
Config:
Additional Information:
New flow created with id 376, packet dispatched to next module
Module information for forward flow ...
snp_fp_tracer_drop
snp_fp_inspect_ip_options
snp_fp_inspect_icmp
snp_fp_translate
snp_fp_adjacency
snp_fp_fragment
snp_ifc_stat

Module information for reverse flow ...

Result:
input-interface: DMZ
input-status: up
input-line-status: up
output-interface: Outside
output-status: up
output-line-status: up
Action: allow

HQ# 
In Phase 1 we find out egress interface.  We only have one, so it's no surprise. In Phase 2 we hit our first NAT rule - out 10.1.1.0/24 to their 10.200.1.0/24.

In Phase 3 we check (and pass) out ACLs, and in Phase 4 we perform NAT, again we hit the first NAT rule, translating our 10.1.1.10/24 client address to itself.

In Phases 5, 6 and 7 we perform per-session NAT, check the IP-Options and any QoS - all of these pass.

Phases 8 and 9 are np-inspects, these pass.

Phase 10 is a RPF (Reverse Path Forwarding) check, and this passed, so then its on to the final flow-creation.

So all looks good there, we don't see any failures. However, we can see that the ACL we are hitting is the original one - before we implemented NAT within our VPN tunnel. Therefore the Client ASA will be seeing traffic come over the VPN with an incorrect endpoint address. So lets just pop over to ASDM (because it's much easier) and try moving the order of our NAT statements around.

Before:


After:


Now (thankfully), our DMZ-Client PC can access the Guest-PC:


As a final note, let's have a look at the packet tracer again and see the difference (I have truncated the output this time to make it a bit easier):
HQ# sh nat detail                                                   
Manual NAT Policies (Section 1)
1 (DMZ) to (Outside) source static MyInsideNetwork YouSeeMeAs   destination static TheirRemoteNetwork TheirRemoteNetwork
    translate_hits = 15, untranslate_hits = 15
    Source - Origin: 10.1.1.0/24, Translated: 192.168.1.0/24
    Destination - Origin: 10.200.1.0/24, Translated: 10.200.1.0/24
2 (DMZ) to (Outside) source static MyInsideNetwork MyInsideNetwork   destination static TheirRemoteNetwork TheirRemoteNetwork no-proxy-arp route-lookup
    translate_hits = 0, untranslate_hits = 0
    Source - Origin: 10.1.1.0/24, Translated: 10.1.1.0/24
    Destination - Origin: 10.200.1.0/24, Translated: 10.200.1.0/24

Manual NAT Policies (Section 3)
1 (DMZ) to (Outside) source dynamic any interface  
    translate_hits = 66, untranslate_hits = 59
    Source - Origin: 0.0.0.0/0, Translated: 1.1.1.2/24
HQ# packet-tracer input DMZ icmp 10.1.1.10 1 7 10.200.1.10 detailed 

Phase: 1
Type: UN-NAT
Subtype: static
Result: ALLOW
Config:
nat (DMZ,Outside) source static MyInsideNetwork YouSeeMeAs destination static TheirRemoteNetwork TheirRemoteNetwork
Additional Information:
NAT divert to egress interface Outside
Untranslate 10.200.1.10/0 to 10.200.1.10/0

Phase: 2
Type: ACCESS-LIST
Subtype: log
Result: ALLOW
Config:
access-group DMZ_access_in in interface DMZ
access-list DMZ_access_in extended permit object-group DM_INLINE_SERVICE_1 any any 
object-group service DM_INLINE_SERVICE_1
 service-object ip 
 service-object icmp 
 service-object icmp echo
 service-object icmp echo-reply

Phase: 3
Type: NAT
Subtype: 
Result: ALLOW
Config:
nat (DMZ,Outside) source static MyInsideNetwork YouSeeMeAs destination static TheirRemoteNetwork TheirRemoteNetwork
Additional Information:
Static translate 10.1.1.10/0 to 192.168.1.10/0

Phase: 4
Type: NAT     
Subtype: per-session
Result: ALLOW

Phase: 5
Type: IP-OPTIONS
Subtype: 
Result: ALLOW

Phase: 6
Type: QOS
Subtype: 
Result: ALLOW

Phase: 7
Type: INSPECT
Subtype: np-inspect
Result: ALLOW

Phase: 8
Type: INSPECT
Subtype: np-inspect
Result: ALLOW
              
Phase: 9
Type: VPN
Subtype: encrypt
Result: ALLOW

Phase: 10
Type: NAT
Subtype: rpf-check
Result: ALLOW
Config:
nat (DMZ,Outside) source static MyInsideNetwork YouSeeMeAs destination static TheirRemoteNetwork TheirRemoteNetwork

Phase: 11
Type: FLOW-CREATION
Subtype: 
Result: ALLOW
Config:
Additional Information:
New flow created with id 392, packet dispatched to next module
Module information for forward flow ...
snp_fp_tracer_drop
snp_fp_inspect_ip_options
snp_fp_inspect_icmp
snp_fp_translate
snp_fp_adjacency
snp_fp_encrypt
snp_fp_fragment
snp_ifc_stat

Module information for reverse flow ...
              
Result:
input-interface: DMZ
input-status: up
input-line-status: up
output-interface: Outside
output-status: up
output-line-status: up
Action: allow

HQ# 

So, here we can see that the order of NAT is extremely important.

Hope you have enjoyed the post!